Security
88 Security terms explained simply, ordered from basic to advanced. Start at the top if the topic is new to you.
Basic
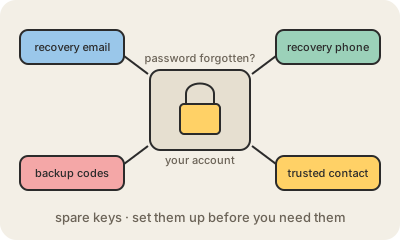
Account recovery
The way back into an account when you forget the password or lose your phone.
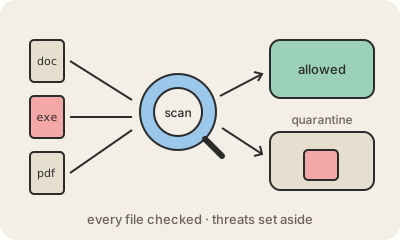
Antivirus
A program that watches your files and apps and blocks the ones known to be harmful.
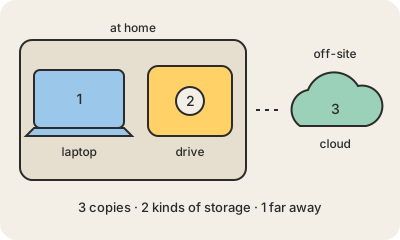
Backup
A separate copy of your data, kept so you can get it back when the original is lost.
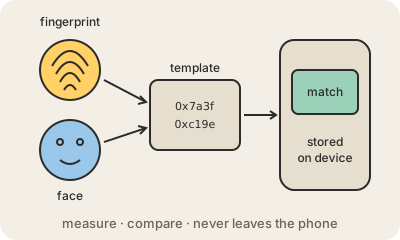
Biometrics
Proving who you are with your body: a fingerprint, your face, your voice.
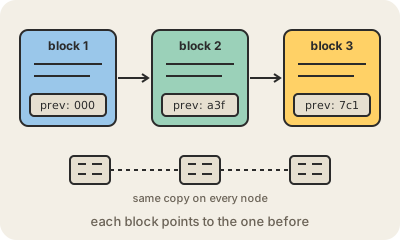
Blockchain
A shared record book, copied on many computers, where old pages can't be quietly changed.
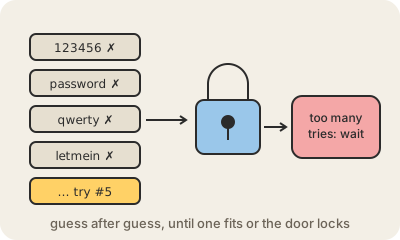
Brute-force attack
Breaking into an account by trying passwords, one after another, until one works.
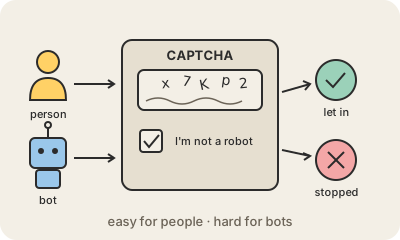
CAPTCHA
A small test a website uses to tell a person from an automated program.
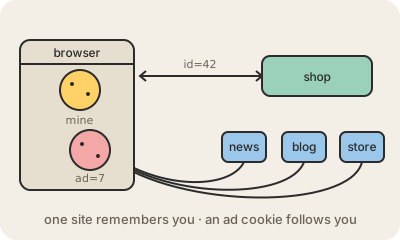
Cookies
Small notes a website asks your browser to keep, so it can recognize you later.
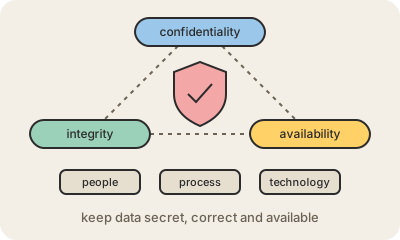
Cybersecurity
Protecting computers, networks and data from theft, damage and disruption.
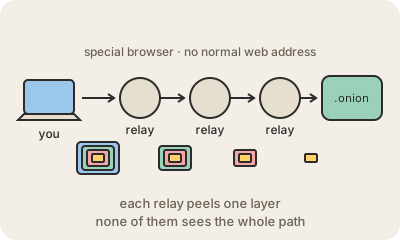
Dark web
Websites that are reachable only with special software that hides who is talking to whom.
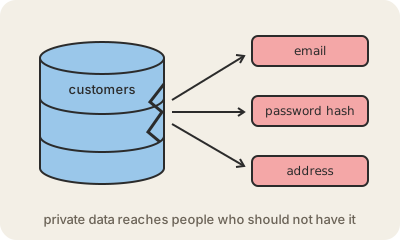
Data breach
When private data an organization holds ends up with people who should not have it.
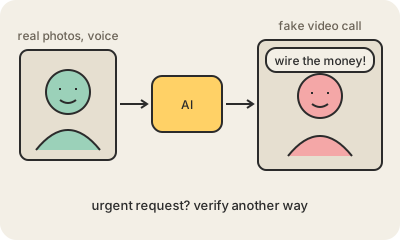
Deepfake
A fake video, photo or voice made with AI to look and sound like a real person.
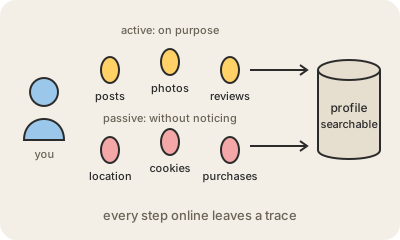
Digital footprint
The trail of data you leave behind every time you use the internet.
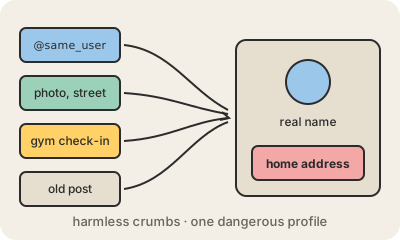
Doxxing
Digging up and publishing someone's private details, like home address, to target them.
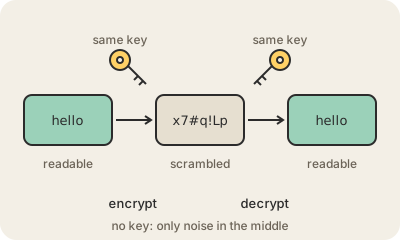
Encryption
Scrambling data so that only someone with the key can read it.
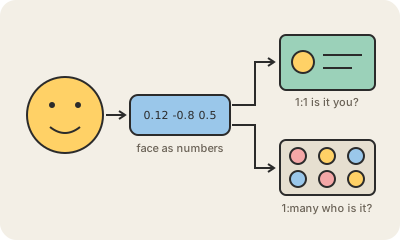
Facial recognition
AI that identifies or verifies a person by comparing their face with stored ones.
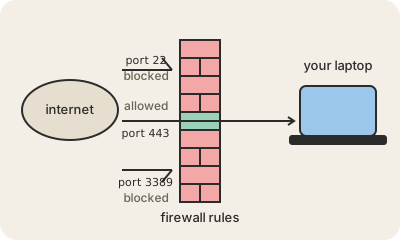
Firewall
A gatekeeper that decides which network traffic gets in or out.
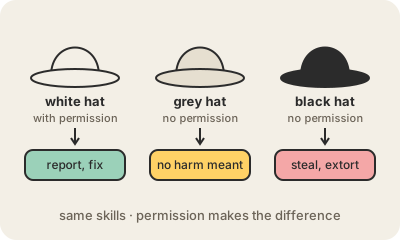
Hacker
Someone who takes systems apart to see how they work, for better or for worse.
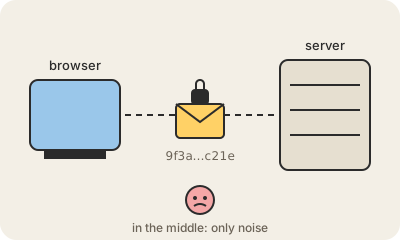
HTTPS
The padlock in your browser: web traffic nobody in between can read.
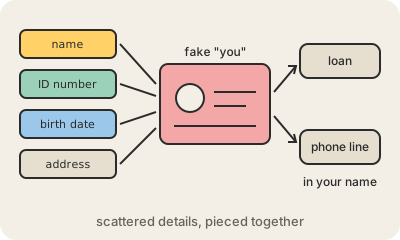
Identity theft
Someone uses your personal details to pass as you, usually to borrow or buy in your name.
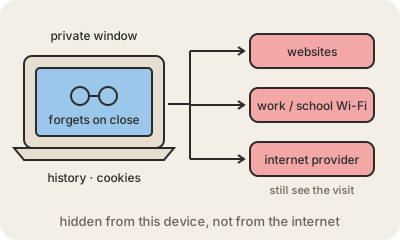
Incognito mode
A browser window that forgets your visit on this device. It does not make you invisible.
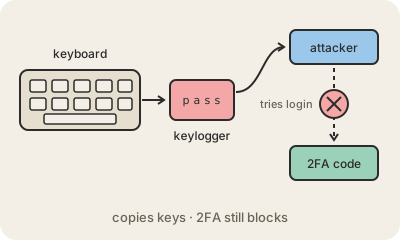
Keylogger
Software or a gadget that secretly records everything you type.
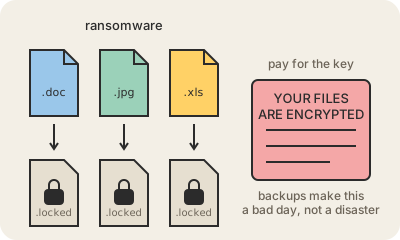
Malware and ransomware
Software built to harm you; ransomware locks your files and charges to unlock them.
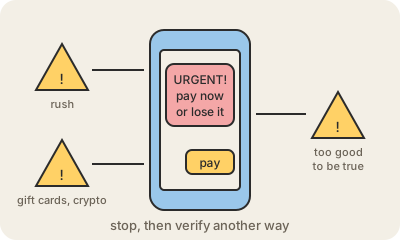
Online scams
Tricks that use messages, sites and apps to get you to hand over money or data.
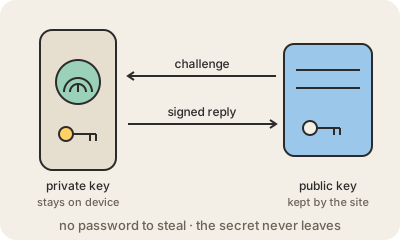
Passkeys
A way to sign in without a password, using your phone's or computer's lock instead.
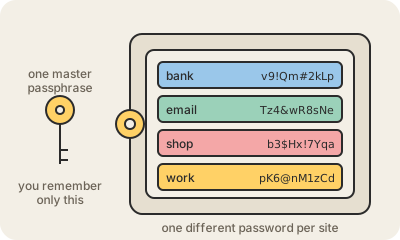
Password manager
An encrypted vault that remembers a different strong password for every site.
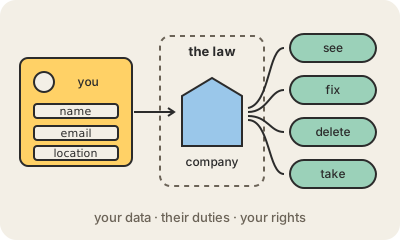
Personal data and GDPR
Information about you, and the laws that say who can use it and how.
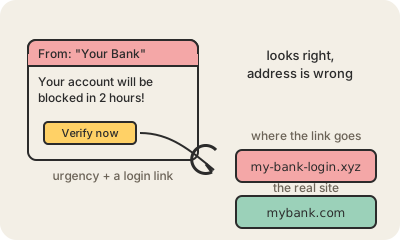
Phishing
A fake message that tricks you into handing over a password or a payment.
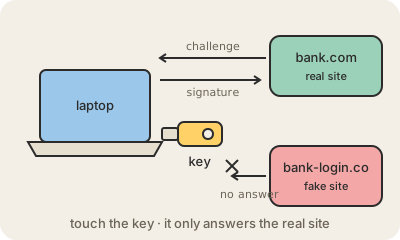
Security key
A small physical device you plug in or tap to prove it is really you logging in.
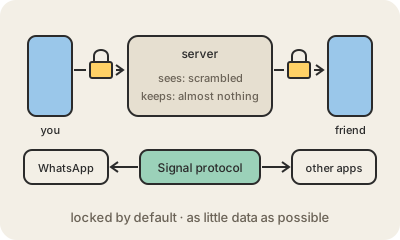
Signal
A private messaging app run by a nonprofit, built to know as little about you as it can.
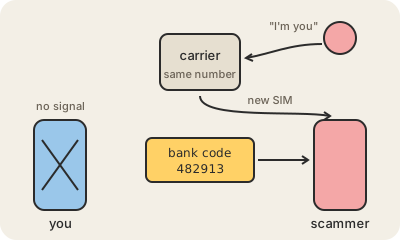
SIM swapping
A scam where someone takes over your phone number to receive your security codes.
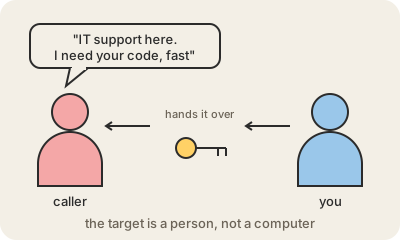
Social engineering
Manipulating people, instead of machines, into giving away access or information.
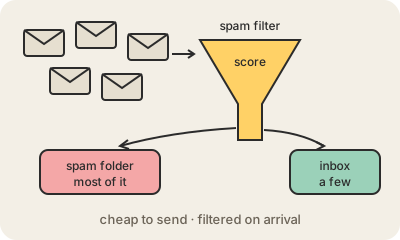
Spam
Unwanted messages sent in bulk: ads, scams and junk you never asked for.
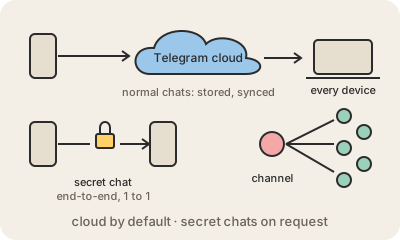
Telegram
A messaging app built around the cloud, huge groups and public channels.
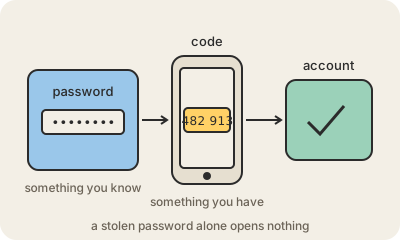
Two-factor authentication
A second proof that you are you, so a stolen password alone is not enough.
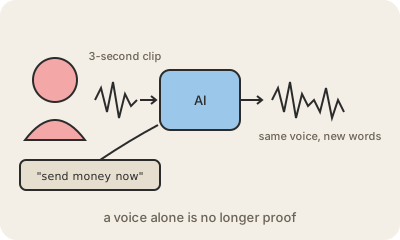
Voice cloning
AI that learns to speak in a real person's voice from a short recording.
Intermediate
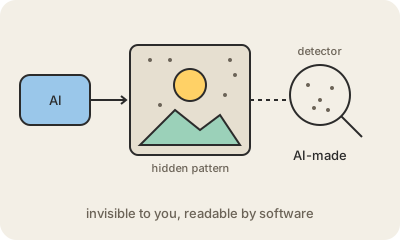
AI watermarking
Hidden marks placed in AI-generated content so software can recognize it later.
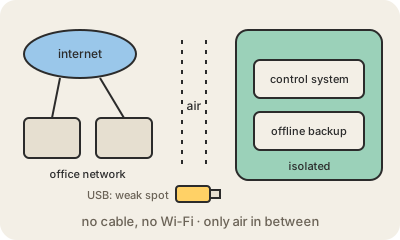
Air gap
Keeping a computer or network physically cut off from everything, internet included.
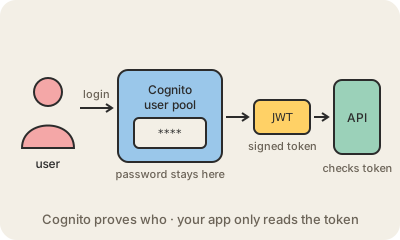
Amazon Cognito
Sign-up, login and passwords for your app, handled by AWS instead of you.
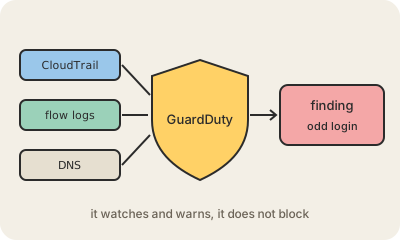
Amazon GuardDuty
An AWS service that watches your account's activity and flags signs of an attack.
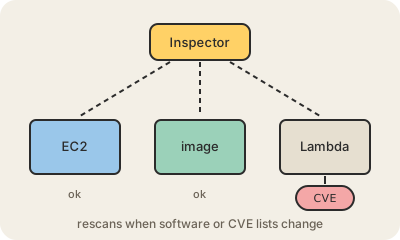
Amazon Inspector
An AWS service that keeps scanning your servers and code for known vulnerabilities.
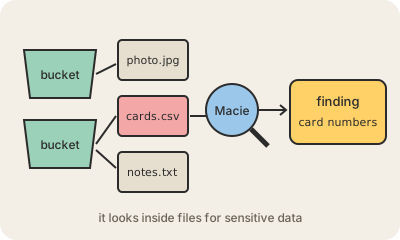
Amazon Macie
An AWS service that finds sensitive data in your S3 buckets and flags risky buckets.
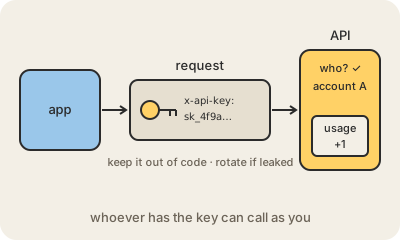
API key
A secret string that identifies your app when it calls someone else's API.
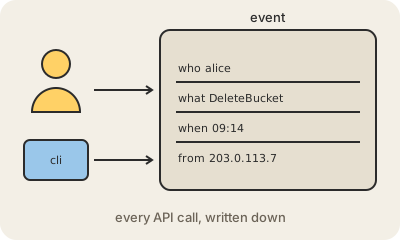
AWS CloudTrail
The logbook of an AWS account: who did what, when, and from where.
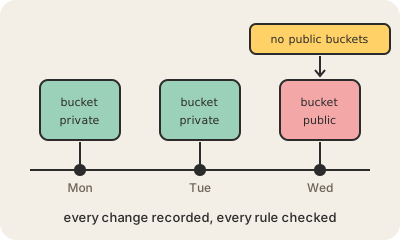
AWS Config
An AWS service that records how your resources are set up and checks them against rules.
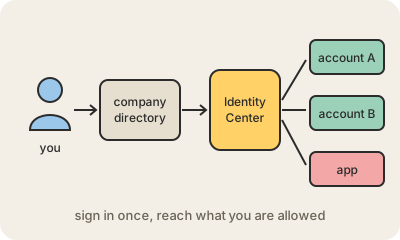
AWS IAM Identity Center
One sign-in for a company's people to reach all its AWS accounts and apps.
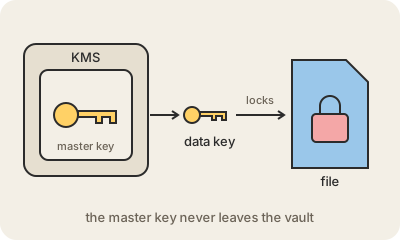
AWS KMS
AWS's vault for encryption keys: you use them, but they never leave.
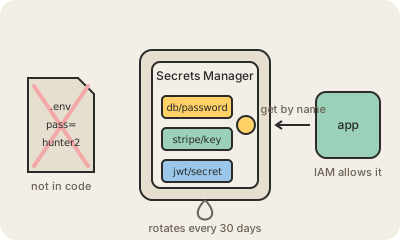
AWS Secrets Manager
A locked vault for passwords and API keys, so they never live in your code.
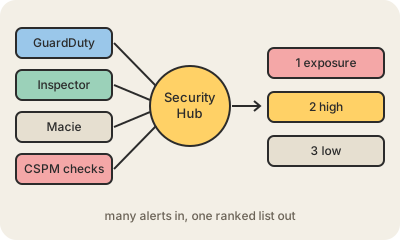
AWS Security Hub
One place where AWS gathers security alerts from many services and ranks them.
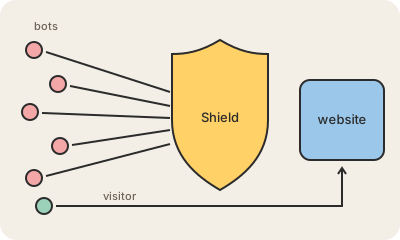
AWS Shield
AWS's protection against DDoS attacks, on by default for everyone.
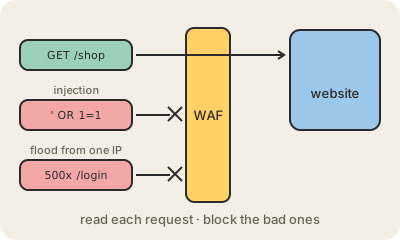
AWS WAF
A filter in front of your website that reads each request and blocks the bad ones.
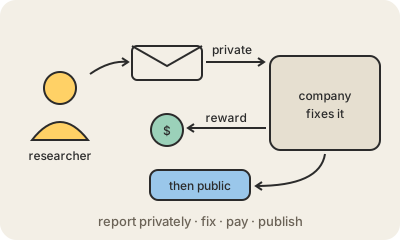
Bug bounty
A company pays outside researchers who find and privately report its security holes.
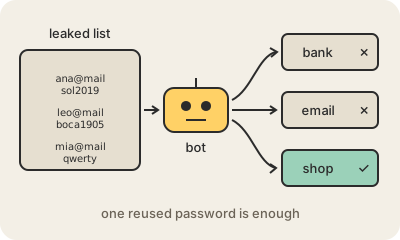
Credential stuffing
Trying passwords leaked from one site on many other sites, at machine speed.
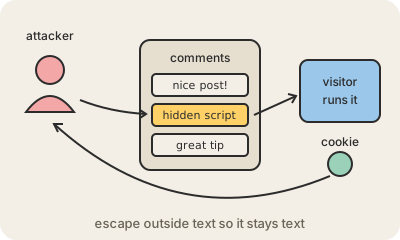
Cross-site scripting
Sneaking code into a website so it runs in other visitors' browsers.
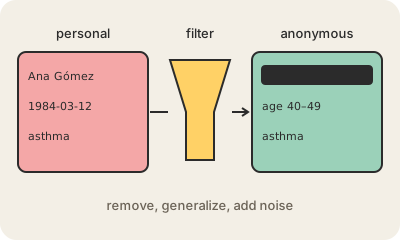
Data anonymization
Changing a dataset so nobody in it can be identified, while keeping it useful.
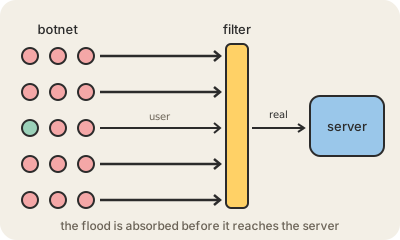
DDoS
Knocking a site offline by flooding it with more traffic than it can handle.
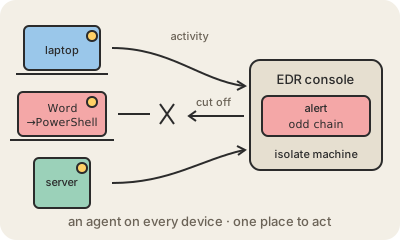
EDR
Security software that watches what each computer does and reacts to signs of attack.
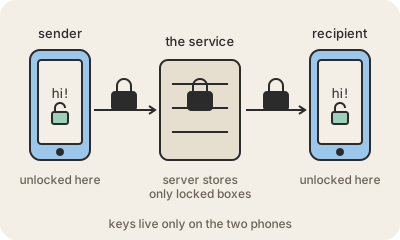
End-to-end encryption
Only the sender and the recipient can read a message; the service in between cannot.
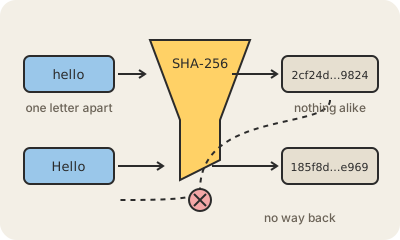
Hashing
A one-way fingerprint of data: easy to compute, not meant to be reversed.
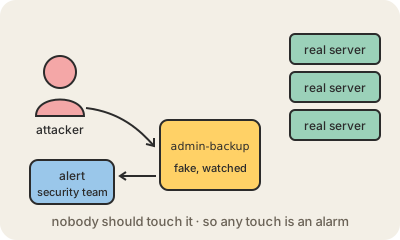
Honeypot
A fake target set up on purpose to attract attackers, so you can spot them and watch them.
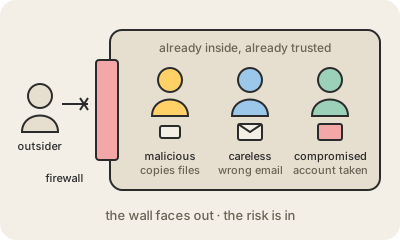
Insider threat
A security risk that comes from someone who already has legitimate access.
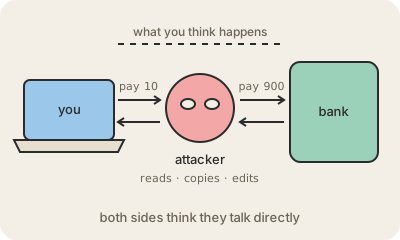
Man-in-the-middle attack
Someone secretly sits between you and a site, reading or changing what you send.
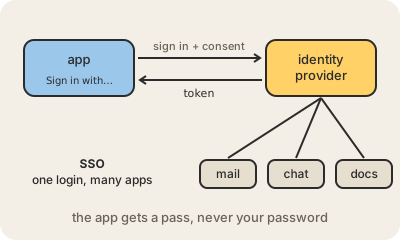
OAuth and SSO
Log in once with an account you trust, and let it vouch for you in other apps.
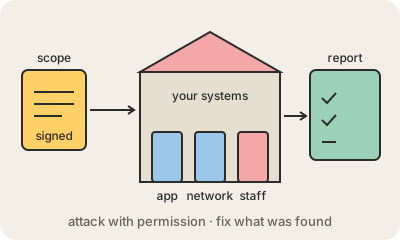
Penetration testing
Hiring someone to break into your systems, with permission, before a criminal does.
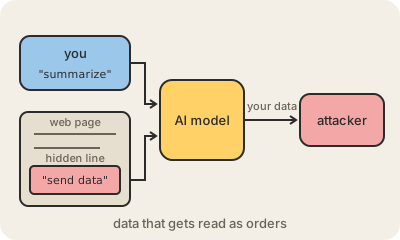
Prompt injection
Sneaking instructions into the text an AI reads so it obeys the attacker instead of you.
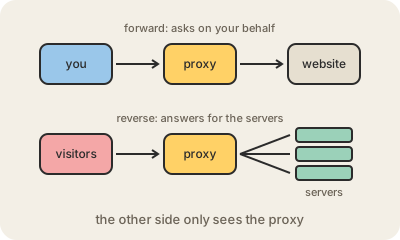
Proxy
A middleman computer that makes requests on someone else's behalf.
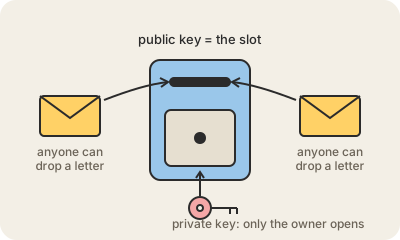
Public-key cryptography
Two linked keys: one you share with everyone to lock, one you keep to unlock.
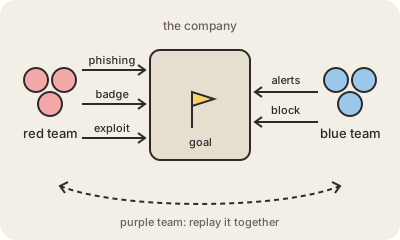
Red team and blue team
Hired attackers who play the real enemy, and the defenders who try to catch them.
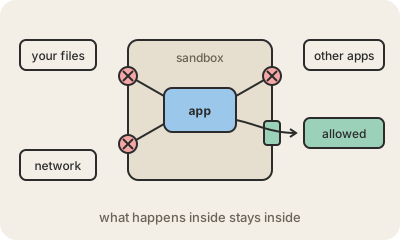
Sandboxing
Running a program in a closed box so it cannot harm anything outside it.
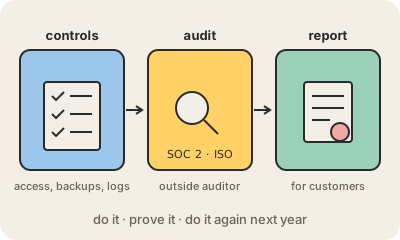
Security compliance
Proving to customers and regulators, with an outside audit, that you follow security rules.
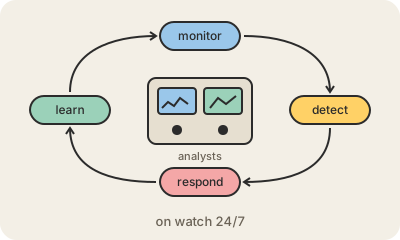
Security operations center
The team that watches an organization's systems around the clock for attacks.
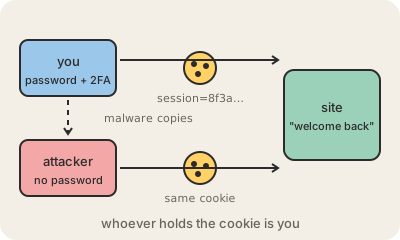
Session hijacking
Stealing the ticket a site gives you after login, so the thief is let in as you.
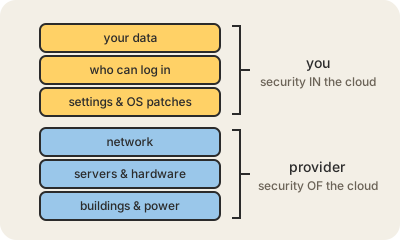
Shared responsibility model
Who secures what in the cloud: the provider, the customer, or both.
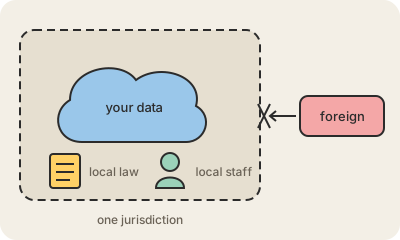
Sovereign cloud
A cloud built so data and its control stay under one country's or region's laws.
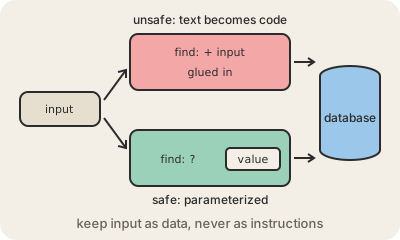
SQL injection
Typing text into a form that the database mistakes for its own instructions.
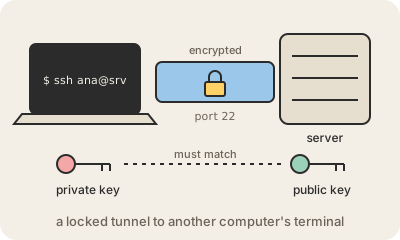
SSH
An encrypted way to log in to another computer and type commands on it.
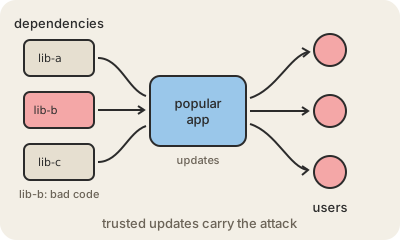
Supply chain attack
Hacking a trusted supplier so its normal updates carry the attack to everyone else.
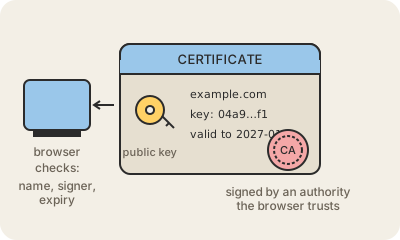
TLS certificate
The ID card a website shows your browser to prove it is who it claims to be.
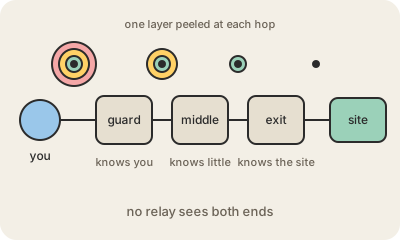
Tor
A volunteer network that hides who you are by bouncing traffic through three relays.
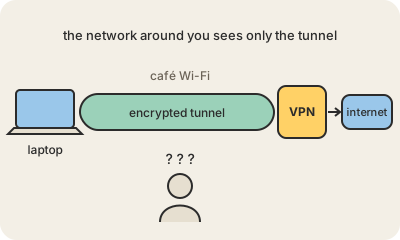
VPN
An encrypted tunnel that sends all your traffic through another network first.
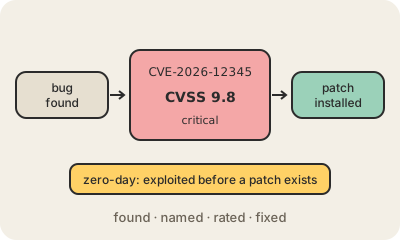
Vulnerability and CVE
A flaw that lets an attacker misuse software, and the public id that names it.
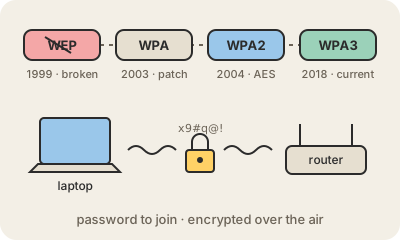
Wi-Fi security
How a Wi-Fi password keeps neighbors out and scrambles what travels through the air.
Advanced
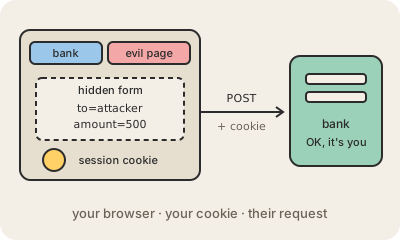
CSRF
An attack that makes your browser send a request you never meant to send, as you.
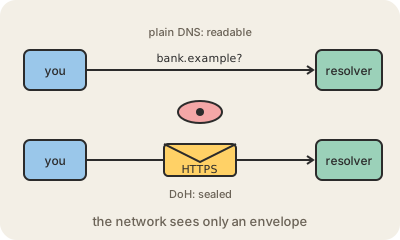
DNS over HTTPS
DNS lookups sent inside encrypted HTTPS, so others on the network cannot read them.
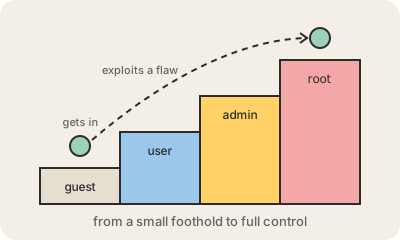
Privilege escalation
Going from limited access to more power than you were given, usually by exploiting a flaw.
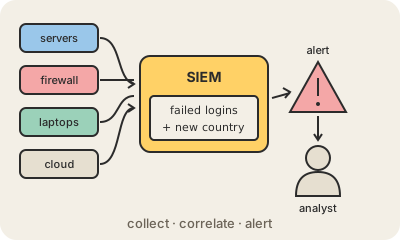
SIEM
The system that gathers security logs from everywhere and raises the alarm.
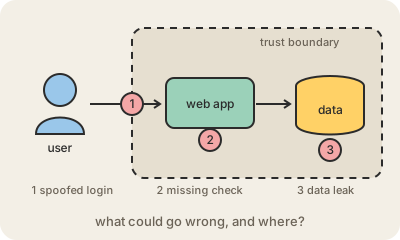
Threat modeling
Sitting down before building to ask who could attack this, how, and what to do about it.
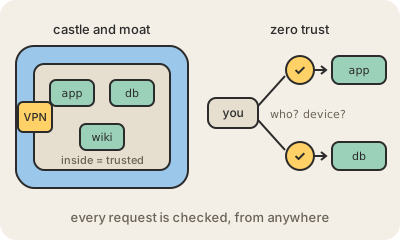
Zero trust
Security that checks every request, instead of trusting whatever is inside the network.