Amazon GuardDuty
An AWS service that watches your account's activity and flags signs of an attack.
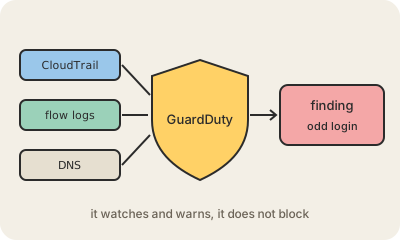
Amazon GuardDuty is a threat detection service for AWS. Once you turn it on, it starts reading the activity logs your account already produces, such as CloudTrail events (who called which API), VPC flow logs (which machines talked to which) and DNS queries, and looks for patterns that suggest something is wrong. You do not install agents or write rules to get started.
When it spots something suspicious it creates a finding: a short report with a type, a severity and the resources involved. Examples are access keys being used from an unusual country, an EC2 instance talking to a known cryptomining server, malware in a file uploaded to S3, or a sequence of small steps that together look like an attacker moving through the account. It combines lists of known bad IP addresses and domains with machine learning that learns what is normal for you.
GuardDuty only detects; it does not block. Teams usually send its findings to an alerting channel or to automation that reacts, for example disabling a leaked key. It complements, rather than replaces, good IAM permissions, AWS WAF in front of web apps, and AWS Config for checking settings.
Keep in mind
- Detects threats by analyzing logs your AWS account already produces.
- Each detection is a finding with a type, severity and affected resources.
- Uses threat intelligence lists plus machine learning about your normal behavior.
- It alerts but does not block; you decide or automate the response.