Privilege escalation
Going from limited access to more power than you were given, usually by exploiting a flaw.
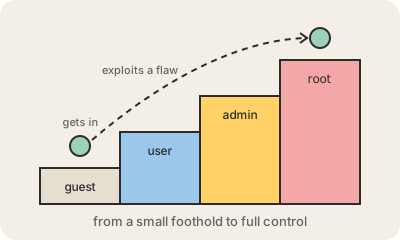
Every system hands out privileges: a normal user can read their own files, an administrator can install software, and root on Linux or SYSTEM on Windows can do anything. Privilege escalation is when someone who got in with limited rights manages to obtain higher ones they were never granted. It is rarely how an attack starts; it is what turns a small foothold, such as a phished employee account or a hacked web app running as a low-privilege service, into control of the whole machine or network.
Vertical escalation climbs up: from user to admin, from a container to the host, from a read-only cloud role to one that can create new credentials. Horizontal escalation moves sideways to another account at the same level, for example changing an ID in a URL to see someone else's invoices. The usual routes are an unpatched kernel or driver vulnerability, a program that runs with high privileges and can be tricked into running the attacker's commands, misconfigured permissions, passwords or keys left in scripts, and in the cloud, IAM policies that let a role grant itself more.
That is why defenders treat it as a separate stage to block, not just the initial break-in. The core ideas are least privilege, so each account and service has only what it needs; prompt patching, since many escalation bugs are public within days; separating admin accounts from everyday ones; and monitoring for the telltale moves, such as a web server process suddenly spawning a root shell. Frameworks like MITRE ATT&CK catalog the known techniques so teams can test their defenses against each one.
Keep in mind
- It turns limited initial access into admin or root control.
- Vertical means climbing to higher rights; horizontal means taking over a peer's account.
- Common routes: unpatched bugs, misconfigured permissions, exposed secrets, over-broad cloud roles.
- Least privilege, fast patching and monitoring limit the damage.
Go deeper
- Privilege escalation on Wikipedia
- MITRE ATT&CK: Privilege Escalation tactic (TA0004)
- CWE-269: Improper Privilege Management