Insider threat
A security risk that comes from someone who already has legitimate access.
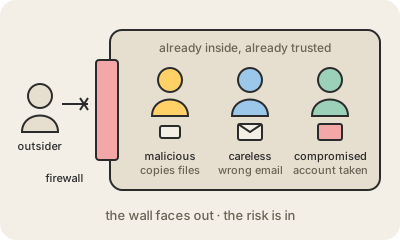
Most defenses are built to keep strangers out: firewalls, passwords, two-factor authentication. An insider threat is the risk that comes from people who are already in: employees, contractors, partners, anyone with a badge or a login. They do not need to break anything, because the system already trusts them.
Insiders come in three flavors. The malicious one acts on purpose: a salesperson who downloads the client list before leaving for a competitor, a disgruntled admin who deletes backups, someone paid to leak secrets. The careless one makes a mistake: emails a spreadsheet full of personal data to the wrong address, leaves a storage bucket public, falls for a phishing email. The compromised one is a real employee whose account has been taken over by an outside attacker, who now looks exactly like an insider.
Defending against insiders is mostly about limits and visibility. Give each person only the access their job needs and remove it the day they leave. Split critical powers so no single person can, say, approve and pay an invoice alone. Log who accesses what, and look for unusual patterns, like someone downloading far more files than usual at 2 a.m. And build a culture where people report mistakes quickly instead of hiding them, since many incidents start as honest errors.
Keep in mind
- Comes from people who already have legitimate access.
- Three kinds: malicious, careless and compromised insiders.
- Least privilege and fast offboarding are the first defenses.
- Logging and spotting unusual behavior catch what permissions miss.